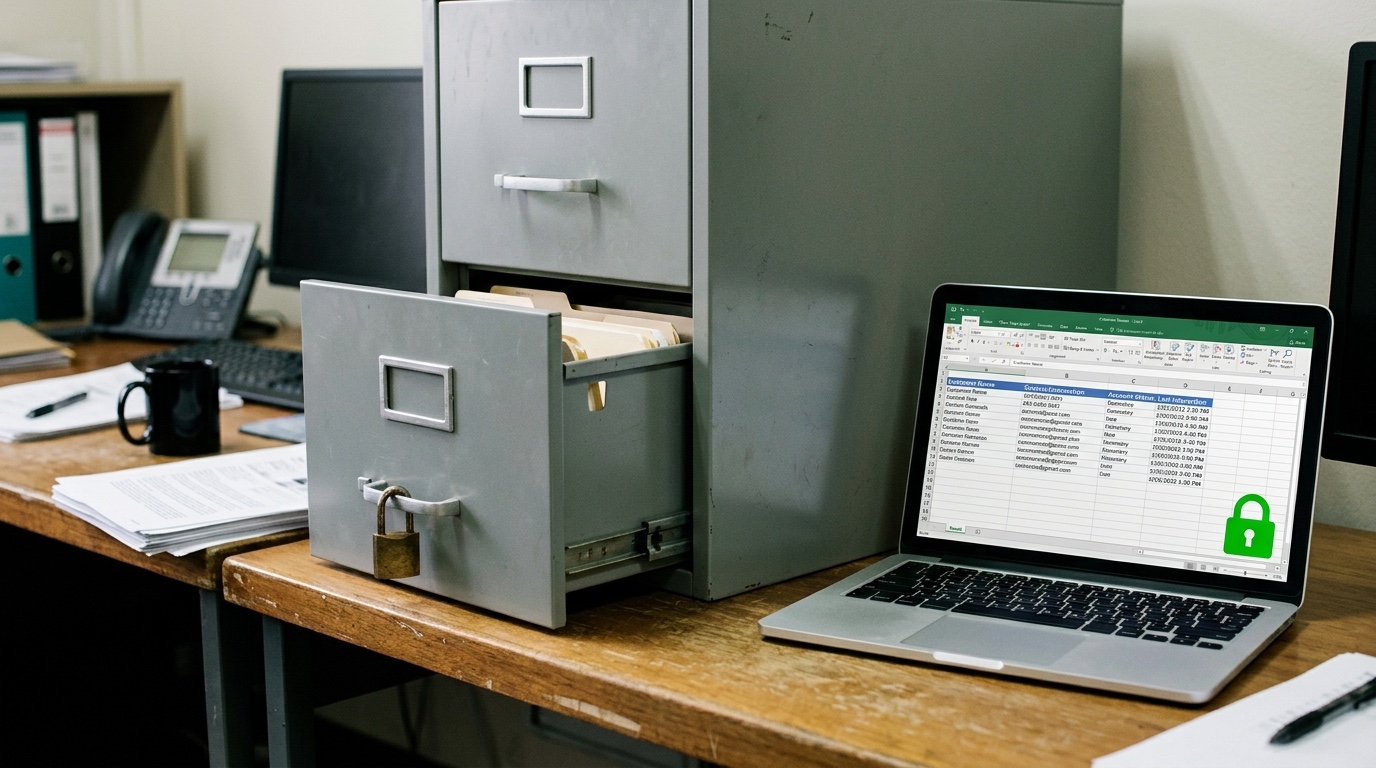
A spreadsheet of names and phone numbers is not automatically a customer strategy. If nobody in the business can explain why the information exists, who's allowed to use it, or when it should be deleted, it isn't a customer asset either—it's a liability with a due date nobody's calendared yet.
As of January 2026, Thailand's Personal Data Protection Committee had logged 2,672 PDPA-related complaints, and among the enforcement cases decided so far, recurring problems include data collected beyond what a stated purpose required, missing data protection officers, and breach notifications filed past the PDPA's 72-hour window. Enersys On August 1, 2025, the PDPC also announced eight administrative fines across five cases totaling roughly THB 21.5 million—including a THB 7 million fine tied to a customer data leak that was later exploited in call-center scams. Tilleke & Gibbins
It's tempting to read that as a legal problem—something for a lawyer to handle once, then file away. It's actually a database design problem that compounds quietly for as long as it's ignored: every field collected without a stated purpose, every export nobody logged, every consent that was assumed rather than recorded, sits on the books as a small liability that grows the longer it goes unaddressed. This is an operational guide, not legal advice—confirm your specific purposes and lawful bases with qualified Thai privacy counsel. It walks through purpose, permission, access, retention, and how to build these habits into a CRM a sales team actually uses every day.
A useful customer database remembers the relationship without forgetting the customer's rights. Every field you can't explain is a debt somebody will eventually have to pay off.
Consent Debt: the liability that builds up one un-purposed field at a time
Call it Consent Debt: the gap between the customer data a business actually holds and the data it can specifically explain—by purpose, by lawful basis, by consent record—if asked tomorrow. Every field added "just in case," every list imported without a documented source, every promotional message sent because a customer once answered a support enquiry, adds a little more to the balance.
Consent Debt is invisible in daily operations, which is exactly what makes it dangerous. Nothing about a bloated customer database with vague permissions looks broken while the business is quietly using it day to day. The debt only becomes visible the way real debt does—at the worst possible moment, usually a data-subject request, a leak, or a regulator's question the business can't answer cleanly. The August 2025 fines show what that moment costs once it arrives: THB 21.5 million across just five cases, spanning a hospital, a retailer, a cosmetics company, and a toy company—industries no more exotic than most Thai SMEs.
Define purpose before fields
Separate sales-enquiry handling, service delivery, billing, support, and marketing as distinct purposes. Document which information each one actually needs and which legal basis applies to it—this single exercise is where most Consent Debt gets paid down, because it forces a business to notice fields nobody can justify.
Do not make promotional consent a condition for answering a basic enquiry when consent isn't necessary for that particular service.
Record permission and source
Keep when, where, and how information was collected, what notice applied at the time, communication preferences, and any withdrawal. ETDA explicitly advises SMEs implementing CRM to prepare for PDPA, and discusses automated communication across LINE, SMS, email, and social media as part of that same guidance. ETDA CRM guidance
Picture a hypothetical gym chain called FitWave Gym, running four branches and a member app across Bangkok. New members signed up through a front-desk tablet, a Facebook lead form, and a walk-in paper form depending on the branch—and each intake method recorded consent differently, when it recorded it at all. When a member later asked what marketing messages they'd agreed to, staff had no reliable way to answer beyond "we'll check." The fix wasn't a stricter sign-up policy; it was one consent record per member, tied to source and date, regardless of which of the three intake methods created it.
Limit access
Use individual accounts and roles rather than one shared login. Sales may need contact and opportunity context; finance may need billing details; marketing shouldn't automatically see sensitive service notes it has no purpose for.
Log exports and remove access the moment roles change. A shared spreadsheet rarely resigns on the same day the employee does—it just keeps quietly existing on a personal laptop somewhere.
Set quality and retention rules
Define required fields, duplicate matching, correction ownership, and review dates. Retain data according to verified legal and business requirements, then actually delete or anonymize it—across primary systems, exports, and every connected tool, not just the main database.
Prepare rights and incident workflows
Create an intake, identity-verification, search, approval, and response process for data-subject requests. Write an incident path for misdirected messages, exposed exports, or compromised accounts before one happens, not while it's happening.
The Government Platform for PDPA Compliance publishes privacy-notice and compliance resources that can support internal preparation. GPPC-PDPC
Control integrations and exports
List every destination receiving customer data: email tools, LINE integration, ad platforms, accounting, support, spreadsheets, and analytics. Document purpose, fields, transfer method, owner, and deletion behaviour for each one. Since LINE conversations are often where this data first appears, make sure that handoff keeps ownership clear—see why a LINE thread can't double as your customer record.
Use the smallest data set needed for each connection. A campaign tool may need an email address and a segment, not the entire sales history. Restrict bulk export and record who performed it and why.
Clean existing data carefully
Before migration, classify active customers, prospects, former customers, suppliers, and unknown contacts. Find duplicates and records without a defensible source or purpose—these are the clearest form of Consent Debt, and migration is the natural moment to settle them rather than carry them forward. Decide with legal and privacy advisers what can be retained, corrected, suppressed, or removed.
Do not manufacture consent during migration. An empty permission field is a fact to resolve, not a box to fill in with "yes" so the import completes cleanly.
The Consent Debt Playbook
- Purpose Before Field—no field gets added to a customer record until someone can state which purpose it serves and which legal basis applies.
- One Consent, One Timestamp—every consent is recorded with when, where, and how it was given, not assumed from a related but different interaction.
- Access Matches Role—a person's access to customer data matches their current job, reviewed the moment that job changes.
- Quarterly Debt Audit—every quarter, sample records for purpose, access, quality, and retention, the same way a business would review any other outstanding liability.
A neighborhood restaurant running a loyalty-stamp app faces the same Consent Debt as a gym chain—a phone number collected for stamp tracking that quietly gets used for marketing blasts nobody explicitly agreed to is exactly the same category of error, just with smaller stakes per customer and just as real a compliance question if a regulator asks.
Add privacy to daily CRM work
Train users to summarize conversations professionally, avoid recording sensitive opinions, verify recipients before sending, and record stated preferences. Give managers a process for access review, unusual export alerts, and removing departed-user access. For the fuller picture of what else a well-run CRM should track day to day, see our jargon-free CRM guide for Thai SMEs.
Audit samples quarterly for purpose, access, quality, preference, and retention. Track requests, incidents, and overdue deletion jobs the same way a finance team tracks overdue invoices.
A PDPA-ready database isn't a one-time compliance project that gets filed away after a lawyer signs off. It's a set of visible operating decisions that stay useful as channels, campaigns, and employees change around it.
Accountable: what this all comes down to
If there's one word for what actually keeps Consent Debt from accumulating, it's Accountable—not a longer privacy policy, not a bigger legal budget, just being able to name, for any piece of customer data, why it exists, who's allowed to touch it, and when it's due to disappear.
So here's the question worth sitting with: pick five customer records at random from your database right now, and try to explain, for each one, why every field in it exists. If you get stuck on any of them, that's Consent Debt sitting on the books today—not a hypothetical future risk.
FAQ
Is a small Thai SME actually a PDPC enforcement target?
The August 2025 fines included a hospital, a retailer, a cosmetics company, and a toy company—not exclusively large enterprises. Complaint volume, not company size, is what triggers most investigations.
Do we need consent for every piece of customer data we hold?
Not every purpose requires consent as its legal basis—some processing is justified under contract or legitimate interest. What every purpose needs is a documented, defensible basis, whichever one actually applies.
How long should we keep customer data after the relationship ends?
It depends on the purpose and applicable retention requirements, which is exactly why documenting purpose up front matters—without it, there's no defensible answer to "why is this still here."
What's the fastest way to start reducing Consent Debt?
Audit a sample of existing records for purpose and consent source before adding anything new. Fixing what already exists usually surfaces more risk than any new field a business is about to add.
Request a customer-data flow assessment to map what enters the CRM, why it is used, and where controls are missing.